A few dropped packets can stall a water treatment plant — no encryption broken.
Industrial plants are moving their Supervisory Control and Data Acquisition (SCADA) systems to the cloud. This puts the link between on-site equipment and the SCADA out on the public Internet, albeit VPN-encrypted. ICS-Sniper shows that an on-path attacker can disrupt the plant operations by reading only the shape of that encrypted traffic (i.e., packet sizes, timing, and direction) and dropping a small, precisely chosen set of packets.
ICS-Sniper is the work of researchers at the University of British Columbia. This research was funded in part by the National Cybersecurity Consortium of Canada (NCC), the Natural Sciences and Engineering Research Council of Canada (NSERC), and the Digital Research Alliance of Canada (DRAC).
SCADA is the software that synchronizes the distributed processes in a plant. It used to live on-site, on a private network. Increasingly, water, wastewater, and manufacturing operators run it on cloud platforms instead — utilities across the US, Canada, Australia, and New Zealand are among the early adopters.
Lower cost
No SCADA hardware or local IT staff to run at every remote site.
Remote operations
Operators monitor and control geographically spread-out assets from anywhere.
Built-in resilience
Cloud providers offer uptime guarantees that on-site systems can't match at low cost.
The trade-off: Some of the plant's most time-sensitive control traffic now crosses the open Internet. To protect it, operators follow the standard NIST recommendations and AWS playbook — authenticate the endpoints, add a firewall and intrusion detection, wrap the traffic in a VPN, and watch for high-volume denial-of-service. This is exactly the architecture ICS-Sniper targets, and it slips past all four safeguards.
The setup in the wild: PLCs on site, SCADA in the cloud, an encrypted VPN across the Internet — and an adversary who only needs a foothold on one router in between.
The short version
An on-path adversary can degrade a safety-critical plant by dropping under 5% of its packets — and go undetected by today's detectors until the damage is done.
Who
A rogue insider at an ISP, or a nation-state with access to a router on the path — the same foothold behind recent Cisco and Juniper router vulnerabilities.
Where
Outside the plant perimeter, on the public Internet path between the site and its cloud-hosted SCADA.
What
Watch the encrypted VPN flow, learn its rhythm, then drop the right packets at the right moment to desynchronize the process.
Why now
The exposure is new — it only exists once SCADA leaves the plant's private network. And the usual defenses (VPN, firewalls, DoS monitoring) give a false sense of safety against it.
How it works
Encryption hides the payload, not the pattern
PLCs talk to SCADA in a steady, repeating rhythm. Each state of the process has its own burst pattern, and that pattern shifts the moment the process is about to change state. VPN encryption hides the contents, but it can't hide when packets arrive, how big they are, or which way they're going. ICS-Sniper reconstructs the rhythm from that metadata alone.
Where the adversary sits: a single compromised router on the public-Internet hop between the on-site PLCs and the cloud SCADA. From there it watches the encrypted VPN flow and drops packets — without entering either network.
Encrypted VPN flow · Adversary's view
Each PLC sends packet bursts at its own fixed period (P₁, P₂). Therefore, over the shared VPN tunnel, a composite packet burst repeats every superperiod L = LCM(P₁, P₂). A new superperiod burst pattern (amber region) indicates a state transition, so ICS-Sniper flags that whole superperiod as critical (red) and drops it.
Stage 1 — profiling (offline)
Learn the plant's rhythm
ICS-Sniper records the encrypted flow over full operational cycles and recovers the repeating structure, then flags the windows where a state change is coming.
Recovers the superperiod using phase folding on packet timing and sizes
Ranks critical superperiods where the burst pattern shifts
Filters out retransmits and keep-alives — no ground truth needed
Stage 2 — attack (live)
Take the shot
On a later cycle, ICS-Sniper waits for the predicted moment and drops only the payload packets in the two targeted windows — including any retransmissions, so the update never lands.
Hits the superperiod before, and during, a state change
Drops ~20% of packets (unconnected) or 100% (connected)
Breaks the timed hand-off between sub-processes
Superperiod
When several PLCs share one tunnel, their individual rhythms combine into a single repeating pattern. That composite period — the least common multiple of the PLC periods — is the superperiod. Find it, and you can predict when the traffic will change.
Phase folding
A noise-resistant technique borrowed from astronomy for finding a hidden period in messy time-series data. ICS-Sniper applies it to overlap durations, inter-packet gaps, and packet sizes to lock onto the superperiod even under jitter and packet loss.
Critical superperiod
A window where the packet count or the set of packet sizes changes from the previous window — a strong signal that the process is about to switch state. These are the windows worth attacking.
A reproducible testbed for cloud-connected SCADA
Studying this attack needed an ICS testbed where the SCADA runs in the cloud and communicates with the plant's on-site PLCs over a VPN. Such a testbed did not exist when we started our research. So we built our own. Our testbed resembles the setup real utilities are now adopting. We have released the implementation details and the code, so anyone can reproduce the attack and test defenses without a live plant.
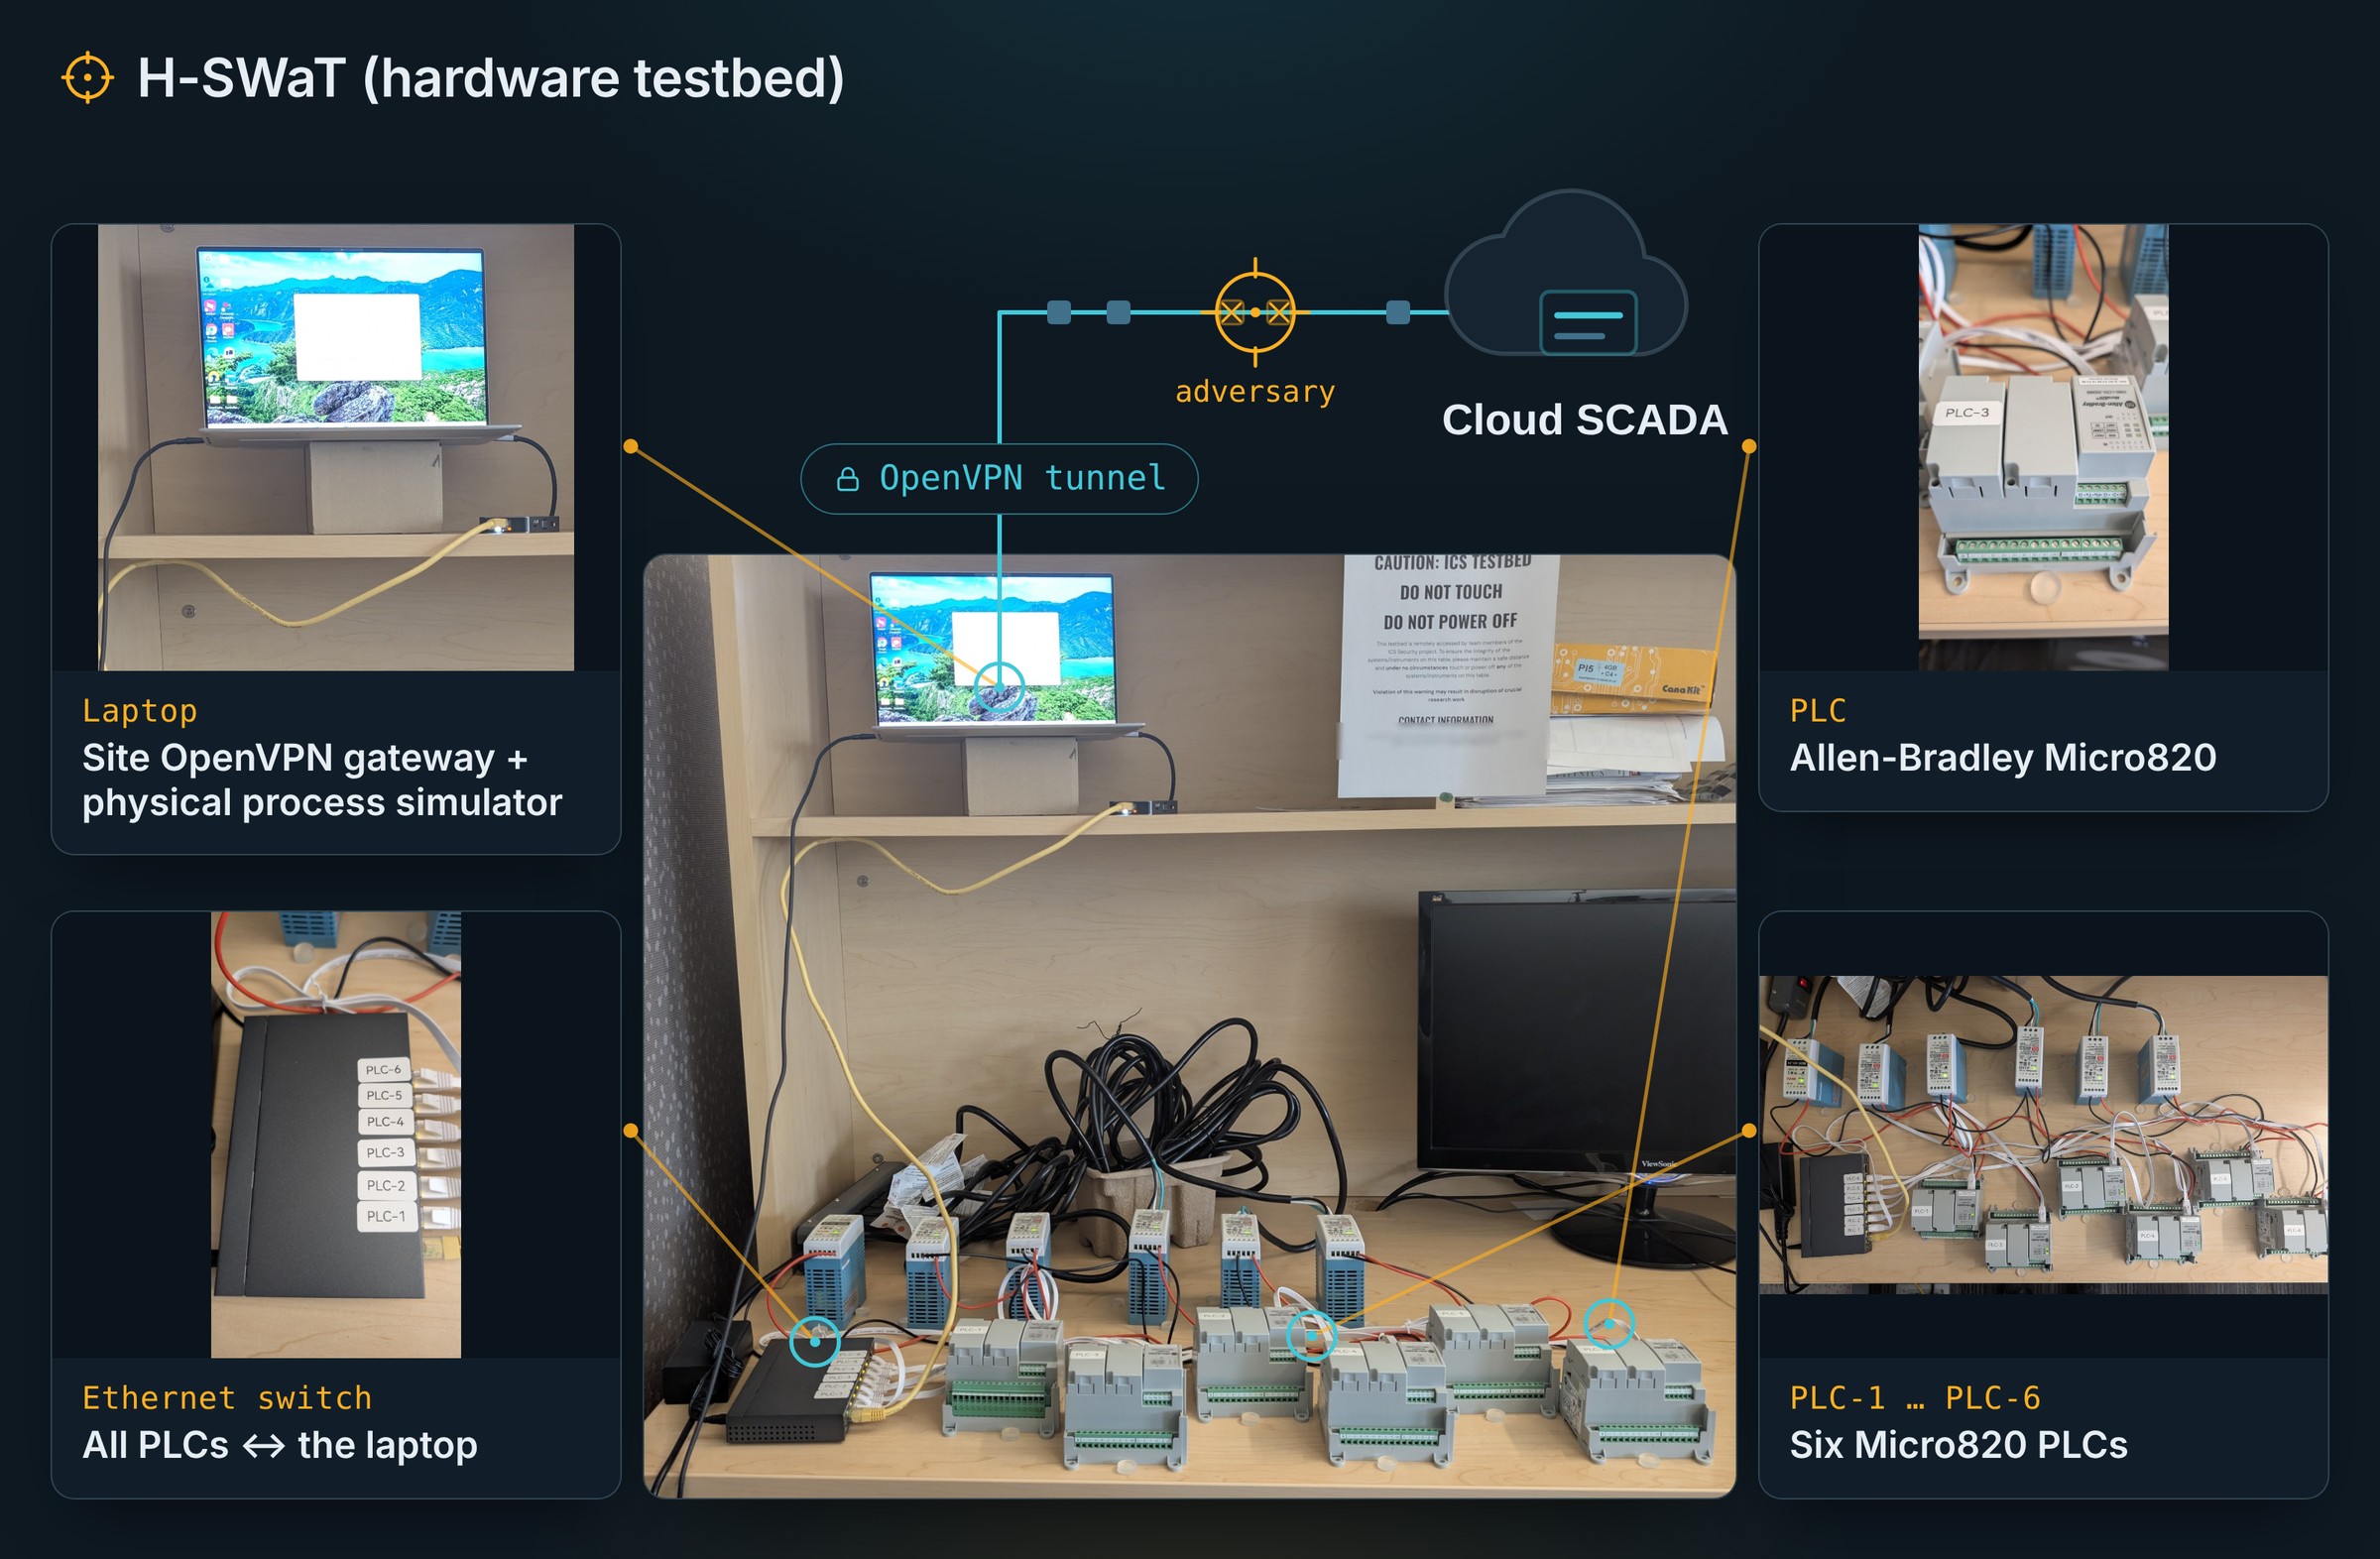
We built two versions of the same six-stage Secure Water Treatment (SWaT) plant setup. One is built with real PLCs, while the other is fully software-simulated. Both versions reproduce the control logic of a multi-stage water-treatment process modeled on SWaT, a widely used reference plant, but host its SCADA in the cloud and carry the site-to-SCADA traffic over OpenVPN. The mechanical process is fully simulated, so no water, pumps, or live equipment are ever involved. The configurations are listed as follows:
hardware · Modbus
H-SWaT
Real Allen-Bradley Micro800 PLCs running connected Modbus/TCP over OpenVPN.
software · Modbus
S-SWaT (Modbus)
Software-simulated PLCs running unconnected Modbus/TCP over OpenVPN.
software · ENIP
S-SWaT (ENIP)
Software-simulated PLCs running unconnected ENIP/TCP over OpenVPN.
Real and simulated controllers. The hardware version runs real Allen-Bradley Micro800 PLCs for realistic timing; the software version runs simulated PLCs for fast experimentation.
Two OT protocols. Modbus/TCP and EtherNet/IP (ENIP), to study whether ICS-Sniper generalizes across OT communication protocols.
Real traffic, safe process. Genuine encrypted VPN traffic and control timing over a simulated physical plant, with no connection to any live system.
Open and reproducible. Released with the captured network traces, so the profiling and detection results reproduce with no special hardware.
Six real PLCs run SWaT's control logic and connect through one switch to a laptop that acts as the site OpenVPN gateway and simulates the physical plant. The SCADA runs on an Amazon EC2 VM, which also acts as the SCADA-side OpenVPN gateway. The site-to-SCADA OpenVPN tunnel is routed through a second EC2 VM that simulates an on-path router compromised by the adversary. The ICS-Sniper code is executed on this VM.
What it does
A quiet attack with real consequences
Demonstrated on realistic water-treatment plants with cloud-hosted SCADA.
Delays clean water
Stalls the plant's core job — producing and pumping purified water on schedule.
Wastes treated water
Breaks tightly-timed hand-offs between stages, draining water the plant already cleaned.
Cuts throughput
The process falls behind, forcing extra runtime or missing its output target.
Evades detection
No monitored detector flags the attack until the plant is already degraded.
In a real plant, these disruptions ripple outward — to the communities and downstream facilities depending on the water — and the whole attack needs nothing more than a foothold on one router along the path. As cloud-hosted SCADA becomes the norm, more plants inherit exactly this exposure.
Why it hides
Built-for-floods detectors don't see an ICS-Sniper attack
An ensemble of eight state-of-the-art ICS detectors — network-based and process-log-based — was trained and run against the attack. In two of five scenarios no detector alerted during the attack at all; in the rest, alerts only arrived after the plant operations had already been degraded.
01
Network detectors fire on packets, not on silence
A short quiet gap on the link — exactly what a dropped burst looks like — triggers nothing. That design is fine for high-rate floods and blind to a targeted blackhole.
02
Nothing conventional defenses look for
No spoofed ARP, no altered payloads, no extra traffic, no volume spike.
03
At least 80% fewer packets than a volumetric attack
ICS-Sniper drops far fewer packets than a naive blackhole aiming for the same effect — and it leaves liveness-check probes untouched, so the link still looks alive.
04
Detection would need a new approach
Catching this likely means actively polling the link in step with each PLC's rhythm — an unsolved research problem, not a setting on an existing tool.
What defenders can do
The attack needs a compromised on-path device to exist — so hardening routers and monitoring the ISP path still matters. Beyond that, the paper points to three directions, none of them fully solved yet.
Shape the traffic (without affecting performance)
open challenge
Diversify the path
So a single compromised hop can't blackhole the flow.
Poll for liveness, on rhythm
open challenge
Code & artifacts
Reproduce it yourself
Everything is open source across five repositories: the attack, the detector ensemble, and three testbeds. Preprocessed traces and SCADA logs ship with the repos, so you can reproduce the profiling and detection results with no live testbed, no special hardware, and no GPU.
# get everything into one folder
git clone https://github.com/ICS-Sniper/ICS-SNIPER-attack.git
git clone https://github.com/ICS-Sniper/SOTA-detectors-NDSS.git
git clone https://github.com/ICS-Sniper/Modbus-C-hardware-testbed.git
git clone https://github.com/ICS-Sniper/Modbus-U-software-testbed.git
git clone https://github.com/ICS-Sniper/ENIP-U-software-testbed.git
With the included traces you can run the profiling and detector steps without setting up a live testbed. Each repository's README has the full setup; the software testbeds and live capture are only needed if you want to reproduce end to end.